Related Topics:
Data Centre Security Access-
Switch Access Security Configuration
Use Strong Passwords: Configure strong, unique passwords for all switch accounts, avoiding default or weak credentials. Enable SSH: Disable insecure protocols like Telnet and enable Secure Shell (SSH) for remote management. Convoluted type 9 secret is supported in Cisco IOS XE Gibraltar 16. 2, you can/may be locked out of the device. Before you downgrade to any. Cisco Meraki MS switches offer the ability to configure access policies, which require connecting devices to authenticate against a RADIUS server before they are granted network access. Control Plane: Control plane consists of the protocols and processes that. Configuring a local Manager password is a fundamental step in reducing the possibility of unauthorized access through the switch WebAgent and console (CLI and Menu) interfaces. Access Security provides different security measures for accessing the switch remotely so as to enhance the configuration management security. This function is used to control the users' access to the switch based on IP address, MAC address or port.
[PDF Version]
-
Aggregation Layer Switch Access Control
Aggregate switches can implement access control lists (ACLs), intrusion detection systems (IDS), and other security measures to protect the entire network from unauthorized access and malicious attacks. They provide a central point for enforcing security policies. An aggregation switch is a network device that consolidates traffic from multiple access switches, wireless access points, or other edge devices and forwards it to core switches or routers. By bundling multiple network connections into a single high-bandwidth link, aggregation switches help. This chapter covers the design recommendations for a data center design deployment consisting of a Cisco Nexus® 7000 Series Switch at the aggregation layer and a Cisco Nexus 5000 Series Switch at the access layer. These switches typically feature multiple 10 Gigabit Ethernet ports and fiber optic connectivity options to ensure sufficient bandwidth for data. The aggregation (sometimes also called distribution) layer is a real crossroad.
[PDF Version]
-
Distance between data center racks
Free online rack space calculator to determine server rack U space requirements, equipment placement, and rack utilization. The cabinet is the transition point between the main and horizontal routes. Server furniture allows housing. My comfort bubble is 3' on either side and the back, and as Gary said, “enough space in front of the rack to have a person working comfortably with a server fully extended. When spacing follows standardized measurements, it allows hardware from different. Proper server rack distance is critical for several reasons: Ventilation and air circulation: Adequate spacing prevents overheating and promotes energy efficiency. Accessibility for maintenance: Enough interval facilitates easier hardware access, aiding maintenance and upgrades. Which standards apply? ANSI/TIA-942, Uptime Institute.
[PDF Version]
-
Security Configuration of Core Switch Ports
This complete port security configuration guide covers sticky MAC address learning, violation modes, troubleshooting err-disabled ports, and advanced security scenarios that networking professionals use daily. If you try to set the maximum value to a number less than the number of secure addresses already configured on an interface, the command is rejected. To understand port security, you should be familiar with how switches learn MAC addresses. Let's. To block unauthorized access to switch ports, switches support a feature called port security. This tutorial explains. In MAC-flooding, an attacker can connect a laptop into an empty Switch port or empty RJ45 wall socket, and he can use hacking tools to generate millions of Ethernet frames with fake source MAC addresses and send them to the switch interface.
[PDF Version]
-
Network security devices IDS
An Intrusion Detection System (IDS) is a security tool that monitors network traffic or system activities to detect unauthorized access or suspicious behavior. Learn how IDS protects an organization's network. Think of it as a "watchdog" that looks for signs of cyber attacks or security breaches, helping administrators respond quickly before. The firewall, IPS, and IDS differ in that the firewall acts as a filter for traffic based on security rules, the IPS actively blocks threats, and the IDS monitors and alerts on potential security breaches.
FAQs about Network security devices IDS
What is an intrusion detection system (IDS)?
An intrusion detection system (IDS) is an application that monitors network traffic and searches for known threats and suspicious or malicious acti...
What are the types of intrusion detection systems (IDS)?
Network intrusion detection system (NIDS), Host intrusion detection system (HIDS), Signature-based intrusion detection system (SIDS), Anomaly-based...
Why are intrusion detection systems (IDS) critical to businesses?
An intrusion detection system provides an extra layer of protection, making it a critical element of an effective cybersecurity strategy.
-
Frequent up down of access switch interfaces
You can use the following commands on CLI to check the status of the interfaces. The Output log lines will show the change of the interface status and help to find if the interface was frequently up and down or not: grep -E "Link. *is (DOWN|UP)" /var/log/ltm* | sed -r 's/^ :]+://g' | . The same port is going up and down many times and it is not about one switch or one user. There are no specific requirements for this document. This document applies to Catalyst switches that run on Cisco IOS® System Software. Is this a normal thing? Should I be troubleshooting layer 1? 3650: Hardware is Gigabit Ethernet, address is 0027. All phones a part of voice VLAN Strangely, when we connect. I am a novice with Cisco switches – I have a switch with some ports that keep oscillating between up and down: Here are the settings on port 1/0/22: How do I diagnose this problem? Post a “show interface fastEthernet 1/0/22” from CLI, or screen from Cisco Network Assistant (interface status, errors.
[PDF Version]
-
SFP Russian network security equipment
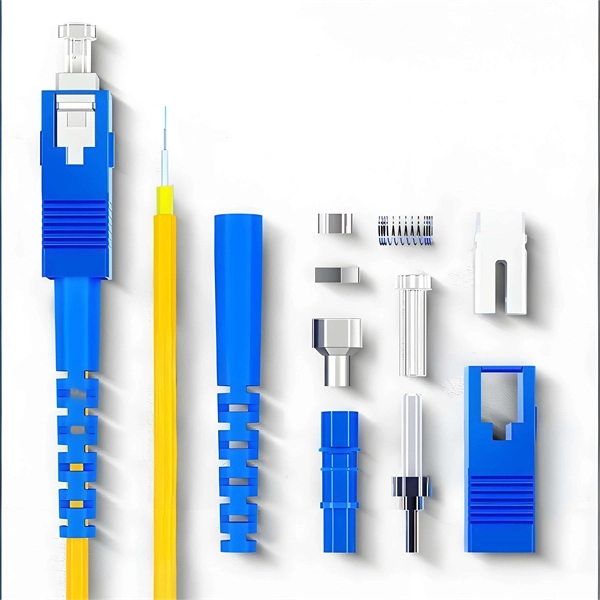
Small Form-factor Pluggable (SFP) is a compact, hot-pluggable network interface module format used for both telecommunication and data communications applications. An SFP interface on networking hardware is a modular slot for a media-specific transceiver, such as for a fiber-optic cable or a copper cable. The advantage of using SFPs compared to fixed interfaces (e.g. modular connector. SFP typesSFP transceivers are available with a variety of transmitter and receiver specifications, allowing users to select the appropriate transceiver for each link to provide the required optical or electrical reach over. Quad Small Form-factor Pluggable (QSFP) transceivers are available with a variety of transmitter and receiver types, allowing users to select the appropriate transceiver for each link to provide the required optical reach over. SFP sockets are found in, routers, firewalls and. They are used in Fibre Channel and storage equipment. Because of their low cost, low profile, and ability to provide a c.
[PDF Version]
-
Is the information security of optical splitters secure
QKD has theoretically been proven to be information-theoretically secure. However, practical QKD systems do not necessarily reach the security level described in theory. The major risk is the possibility of inserting a splitter into the optical distribution network and capturing a portion of the entire spectrum, i. Optical splitters, in their most fundamental form, are passive devices designed to divide an incoming. However, with data transmitted from an optical line terminal (OLT) over a single strand of singlemode fiber through passive splitters, there is some misconception that redundancy, protection, and fault detection to achieve maximum availability, security, and reliability are not fundamental in. We address emerging threats to the security of optical networks, mainly loss of the confidentiality of user data transmitted through optical bers and disturbances of network control, both of which could seriously damage the entire network.
[PDF Version]
-
Functions of the Switch Access Layer
It typically sits at the access layer, provides high port density, often delivers PoE, and forwards traffic upstream to the distribution or core layer. Executive Summary: An access switch is the first network device most users and endpoints actually touch. Other important merits include enhanced security through features like TrustSec, which offers controlled access and network. The Switch is a network device that is used to segment the networks into different subnetworks called subnets or LAN segments. An enterprise network is a large network that may contain several campus networks spanning different. In a typical enterprise network architecture, the access layer switch is the first point of contact between end-user devices and the rest of the network.
[PDF Version]
-
Fiber optic cable only connects to the router for internet access
The fiber optic cable does not plug directly into a standard home router because the signal type must be translated. The fiber line terminates at the Optical Network Terminal (ONT), which is typically supplied and installed by the internet service provider. In this guide, we'll walk you through how to. The process to connect fiber optic cable to router requires careful attention to detail, but I'll walk you through every critical step with the precision and clarity you deserve. You need a modem or ONT to do so. As internet speeds continue to evolve, fiber optic broadband is becoming the gold standard for ultra-fast and reliable internet connections. Fiber optics can transmit data over much longer distances compared to traditional copper cables.
[PDF Version]