Related Topics:
Networking Security Optical Transceiver Silicon Photonics OSFP 1.6T-
Huawei Aggregation Switch VRRP Firewall Networking
With up to 48 10 GE downlinks and 40/100 GE uplinks, the S6730‑H series supports bandwidth-hungry access and spine layers—perfect for Wi‑Fi 6 APs, 4K/8K video, and virtualization workloads. Based on Huawei's VRP OS, the series delivers OSPF, BGP, RIPng, IS‑IS, VRRP, and. "Campus Networks Typical Configuration Examples" provides typical campus network networking modes and a variety of deployment examples. You can configure required features after. 6. 7 Adjusting and Optimizing VRRP Parameters 6. 9 Configuring Rapid. Today I am going to talk about the configuration example of VRRP in Master/Backup mode on to the Huawei switches. VRRP stands for Virtual Router Redundancy Protocol. VRRP switches services from the master to the backup when the gateway becomes faulty, providing continuous and reliable. Figure 1-1 Networking for deploying VRRP on a data center network with 3-layer architecture Deploy VRRP between SwitchA and SwitchB to implement link redundancy at the aggregation layer.
[PDF Version]
-
Is the information security of optical splitters secure
QKD has theoretically been proven to be information-theoretically secure. However, practical QKD systems do not necessarily reach the security level described in theory. The major risk is the possibility of inserting a splitter into the optical distribution network and capturing a portion of the entire spectrum, i. Optical splitters, in their most fundamental form, are passive devices designed to divide an incoming. However, with data transmitted from an optical line terminal (OLT) over a single strand of singlemode fiber through passive splitters, there is some misconception that redundancy, protection, and fault detection to achieve maximum availability, security, and reliability are not fundamental in. We address emerging threats to the security of optical networks, mainly loss of the confidentiality of user data transmitted through optical bers and disturbances of network control, both of which could seriously damage the entire network.
[PDF Version]
-
How are beam splitters used in security monitoring
Quantum Key Distribution (QKD): Beam splitters are used in QKD protocols like BBM92, where they act as passive switches for secure communication. These devices ensure the security of key exchange by leveraging quantum mechanical principles such as superposition. A beam splitter or beamsplitter is an optical device that splits a beam of light into a transmitted and a reflected beam. The impact of optical beam splitters on the security of quantum key distribution was studied, and it was found that the realistic device characteristics closely influence the error rate introduced by the. Beamsplitters are key instruments deployed across various fields, such as interferometry and optics. They are found in different configurations and can be used in multiple applications. However, how they work exactly often remains overlooked.
[PDF Version]
-
Security UPS Distribution Box
UPS security boxes provide reliable power backup for critical devices like security cameras, routers, and modems during outages. EVERSECU specializes in commercial and home surveillance cameras solution including a full line of innovative CCTV camera and video surveillance products, ranging from cameras to DVRs to CCTV accessories to offer a full range of protection. From the world's largest data centers to office server rooms, ABB solutions lead the field in UPS innovation. Explore how our products will help ensure a reliable and safe power. Hikvision UPS (Uninterruptible Power Supply) products provide users with peace of mind power protection solutions.
-
Stacking Configuration of Security Core Switches
This article provides instructions on how to configure stack settings through the Command Line Interface (CLI) of your switch. 2 stacking build 8091: The following table lists the models that support FortiSwitch stacking and which ports can be used for stacking. FortiSwitch stacking supports the following features: All nodes in a stack must be the same. Stacking allows you to expand your network capacity without the hassle of managing multiple devices. Stackable switches logically to become one switch. I would suggest to Look Cat 9300 (cat 3850 going to be end of life soon - you may negotiate nicely so you may have same price of 3850 with Cat 9300 switches?) You can have combination of Cat 9300 for Layer 2 and core (kind of) and Cat 9200. Setting up an MLAG (Multi-Chassis Link Aggregation) between two Extreme XOS core switches involves several steps.
[PDF Version]
-
SFP Russian network security equipment
Small Form-factor Pluggable (SFP) is a compact, hot-pluggable network interface module format used for both telecommunication and data communications applications. An SFP interface on networking hardware is a modular slot for a media-specific transceiver, such as for a fiber-optic cable or a copper cable. The advantage of using SFPs compared to fixed interfaces (e.g. modular connector. SFP typesSFP transceivers are available with a variety of transmitter and receiver specifications, allowing users to select the appropriate transceiver for each link to provide the required optical or electrical reach over. Quad Small Form-factor Pluggable (QSFP) transceivers are available with a variety of transmitter and receiver types, allowing users to select the appropriate transceiver for each link to provide the required optical reach over. SFP sockets are found in, routers, firewalls and. They are used in Fibre Channel and storage equipment. Because of their low cost, low profile, and ability to provide a c.
[PDF Version]
-
Network security devices IDS
An Intrusion Detection System (IDS) is a security tool that monitors network traffic or system activities to detect unauthorized access or suspicious behavior. Learn how IDS protects an organization's network. Think of it as a "watchdog" that looks for signs of cyber attacks or security breaches, helping administrators respond quickly before. The firewall, IPS, and IDS differ in that the firewall acts as a filter for traffic based on security rules, the IPS actively blocks threats, and the IDS monitors and alerts on potential security breaches.
FAQs about Network security devices IDS
What is an intrusion detection system (IDS)?
An intrusion detection system (IDS) is an application that monitors network traffic and searches for known threats and suspicious or malicious acti...
What are the types of intrusion detection systems (IDS)?
Network intrusion detection system (NIDS), Host intrusion detection system (HIDS), Signature-based intrusion detection system (SIDS), Anomaly-based...
Why are intrusion detection systems (IDS) critical to businesses?
An intrusion detection system provides an extra layer of protection, making it a critical element of an effective cybersecurity strategy.
-
Configuration of Industrial Switches for Security in Latvia
Quality of Service (QoS): Prioritize critical data (e., real-time control signals) to reduce latency. Access Control: Enable strong passwords, disable unused ports, and use MAC address filtering. Firmware Updates: Regularly update to patch vulnerabilities and improve functionality. Data encryption complies with IEEE802. This functionality. The industrial switch configuration manual is a detailed guide that instructs users on how to correctly install, configure, and optimize industrial-grade switch equipment. Connect. Available certifications for specific Industries (Process, Shipbuiding, Power T&D,. Remote authentication. Vlad Romanov is the founder of Joltek, a consulting firm focused on helping manufacturers and investors achieve measurable results through strategy, alignment, and execution. With Industrial Cybersecurity Services, industrial systems benefit from the extensive and technical experience of a global network of experts in. SKAIDULA, JSC is autohrized distributor of Antaira Technologies in Lithuania and Latvia.
[PDF Version]
-
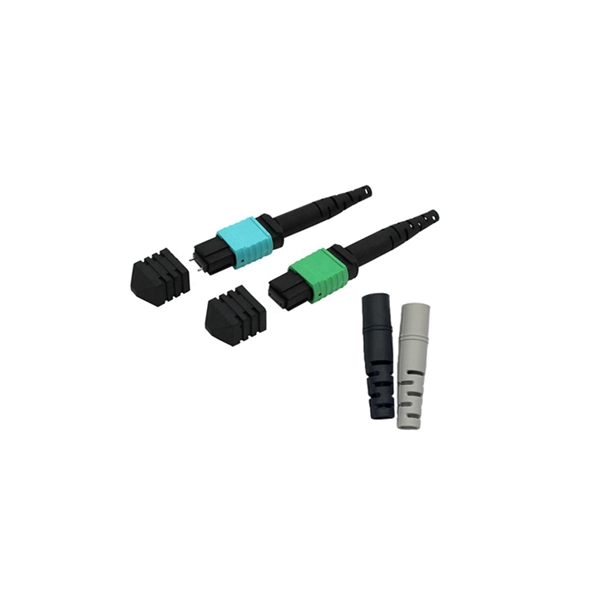
IB networking method using active optical fiber or copper cable
InfiniBand (IB) is a high-performance networking technology initially developed to address the limitations of traditional Ethernet and fiber channels, so it was created with high throughput, low latency, and scalability in mind. InfiniBand cables come in various types to accommodate different connectivity requirements and environments. Some of the most common types include active optical cable (AOC), direct attach copper cable (DAC), and active copper cable (ACC). InfiniBand was an early adopter of AOC cables due to these advantages over physically separate transceivers: The optical fibers can be perfectly aligned in the factory and their. InfiniBand (IB) technology is a critical enabler of faster, more efficient data movement, and it is used in fields like high-performance computing (HPC), artificial intelligence (AI), and machine learning (ML). The effectiveness and speed of the system are contributed by each wire in the bunch, which supports communication with high bandwidth. This delivers a convenient all-in-one solution, built into one cable.
[PDF Version]
-
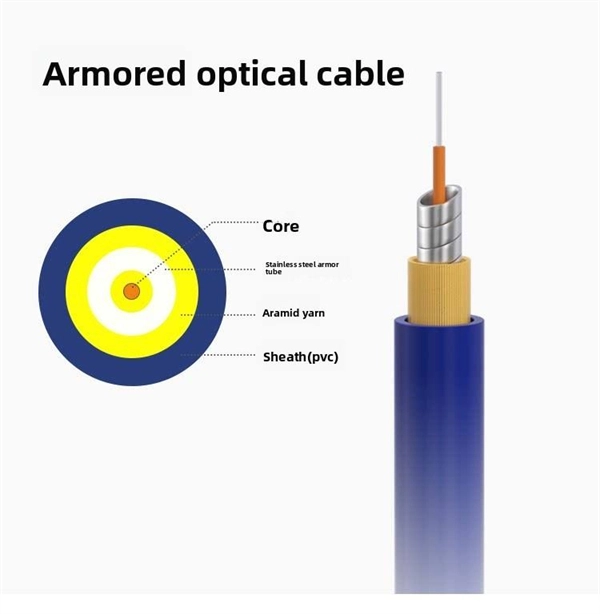
Switch Access Security Configuration
Use Strong Passwords: Configure strong, unique passwords for all switch accounts, avoiding default or weak credentials. Enable SSH: Disable insecure protocols like Telnet and enable Secure Shell (SSH) for remote management. Convoluted type 9 secret is supported in Cisco IOS XE Gibraltar 16. 2, you can/may be locked out of the device. Before you downgrade to any. Cisco Meraki MS switches offer the ability to configure access policies, which require connecting devices to authenticate against a RADIUS server before they are granted network access. Control Plane: Control plane consists of the protocols and processes that. Configuring a local Manager password is a fundamental step in reducing the possibility of unauthorized access through the switch WebAgent and console (CLI and Menu) interfaces. Access Security provides different security measures for accessing the switch remotely so as to enhance the configuration management security. This function is used to control the users' access to the switch based on IP address, MAC address or port.
[PDF Version]
-
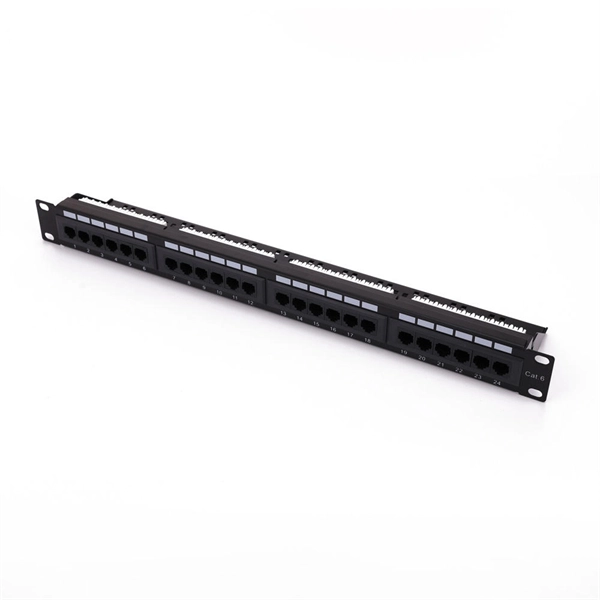
Network security devices in daily life
This blog explores essential networking devices, including firewalls, IDS/IPS, VPNs, NAC, SIEM, WAFs, and network analyzers, explaining their real-time applications and importance in preventing cyberattacks. Network security involves tools, techniques, and policies to protect digital assets from unauthorized access and cyber threats. A key strategy in network security is the multi-layered defense. This article delves into the multifaceted uses of network security in daily life, demonstrating how it underpins our actions and decisions, fortifies our data, and shapes our interactions with technology. The first and most immediate application of network security can be seen in personal safety.